Skip to content
📣 Integrity Security Services (ISS) is now OmniTrust.
Read our CEO’s Letter ->
Contact Us
Home
Resources
Blog
Tag: EU CRA Compliance
tag
EU CRA Compliance
All EU CRA Compliance Blogs
EU CRA Tales From The Trenches #9 – Open Source Software is Now a Boardroom Issue
Executive Viewpoints
,
Industry Insights
,
Lifecycle Lessons
,
Trust Lifecycle Management
NP
Nick Parnaby
September 11, 2026
EU CRA Tales From The Trenches #8 – Your Suppliers May Be Your Biggest Compliance Risk
Executive Viewpoints
,
Industry Insights
,
Lifecycle Lessons
,
Trust Lifecycle Management
NP
Nick Parnaby
September 1, 2026
EU CRA Tales From The Trenches #7 – CRA Compliance Requires Enterprise-Wide Coordination
Executive Viewpoints
,
Industry Insights
,
Lifecycle Lessons
,
Trust Lifecycle Management
NP
Nick Parnaby
August 21, 2026
EU CRA Tales From The Trenches #6 – Waiting for Finalized Standards is not a Strategy, It’s a Recipe for Failure
Executive Viewpoints
,
Industry Insights
,
Lifecycle Lessons
,
Trust Lifecycle Management
NP
Nick Parnaby
August 10, 2026
EU CRA Tales From The Trenches #5 – The 24-Hour Reporting Clock is Really a Visibility Problem
Executive Viewpoints
,
Industry Insights
,
Lifecycle Lessons
,
Trust Lifecycle Management
NP
Nick Parnaby
July 23, 2026
EU CRA Tales From The Trenches #4 – The Real Work for CRA Compliance Starts After Product Release
Executive Viewpoints
,
Industry Insights
,
Lifecycle Lessons
,
Trust Lifecycle Management
NP
Nick Parnaby
July 15, 2026
🔨 We Came to Hang One Picture… Somehow We Ended Up Talking About Product Cyber Risk & Compliance
Executive Viewpoints
,
Threat, Risk & Vulnerability
,
Trust Lifecycle Management
NP
Nick Parnaby
July 15, 2026
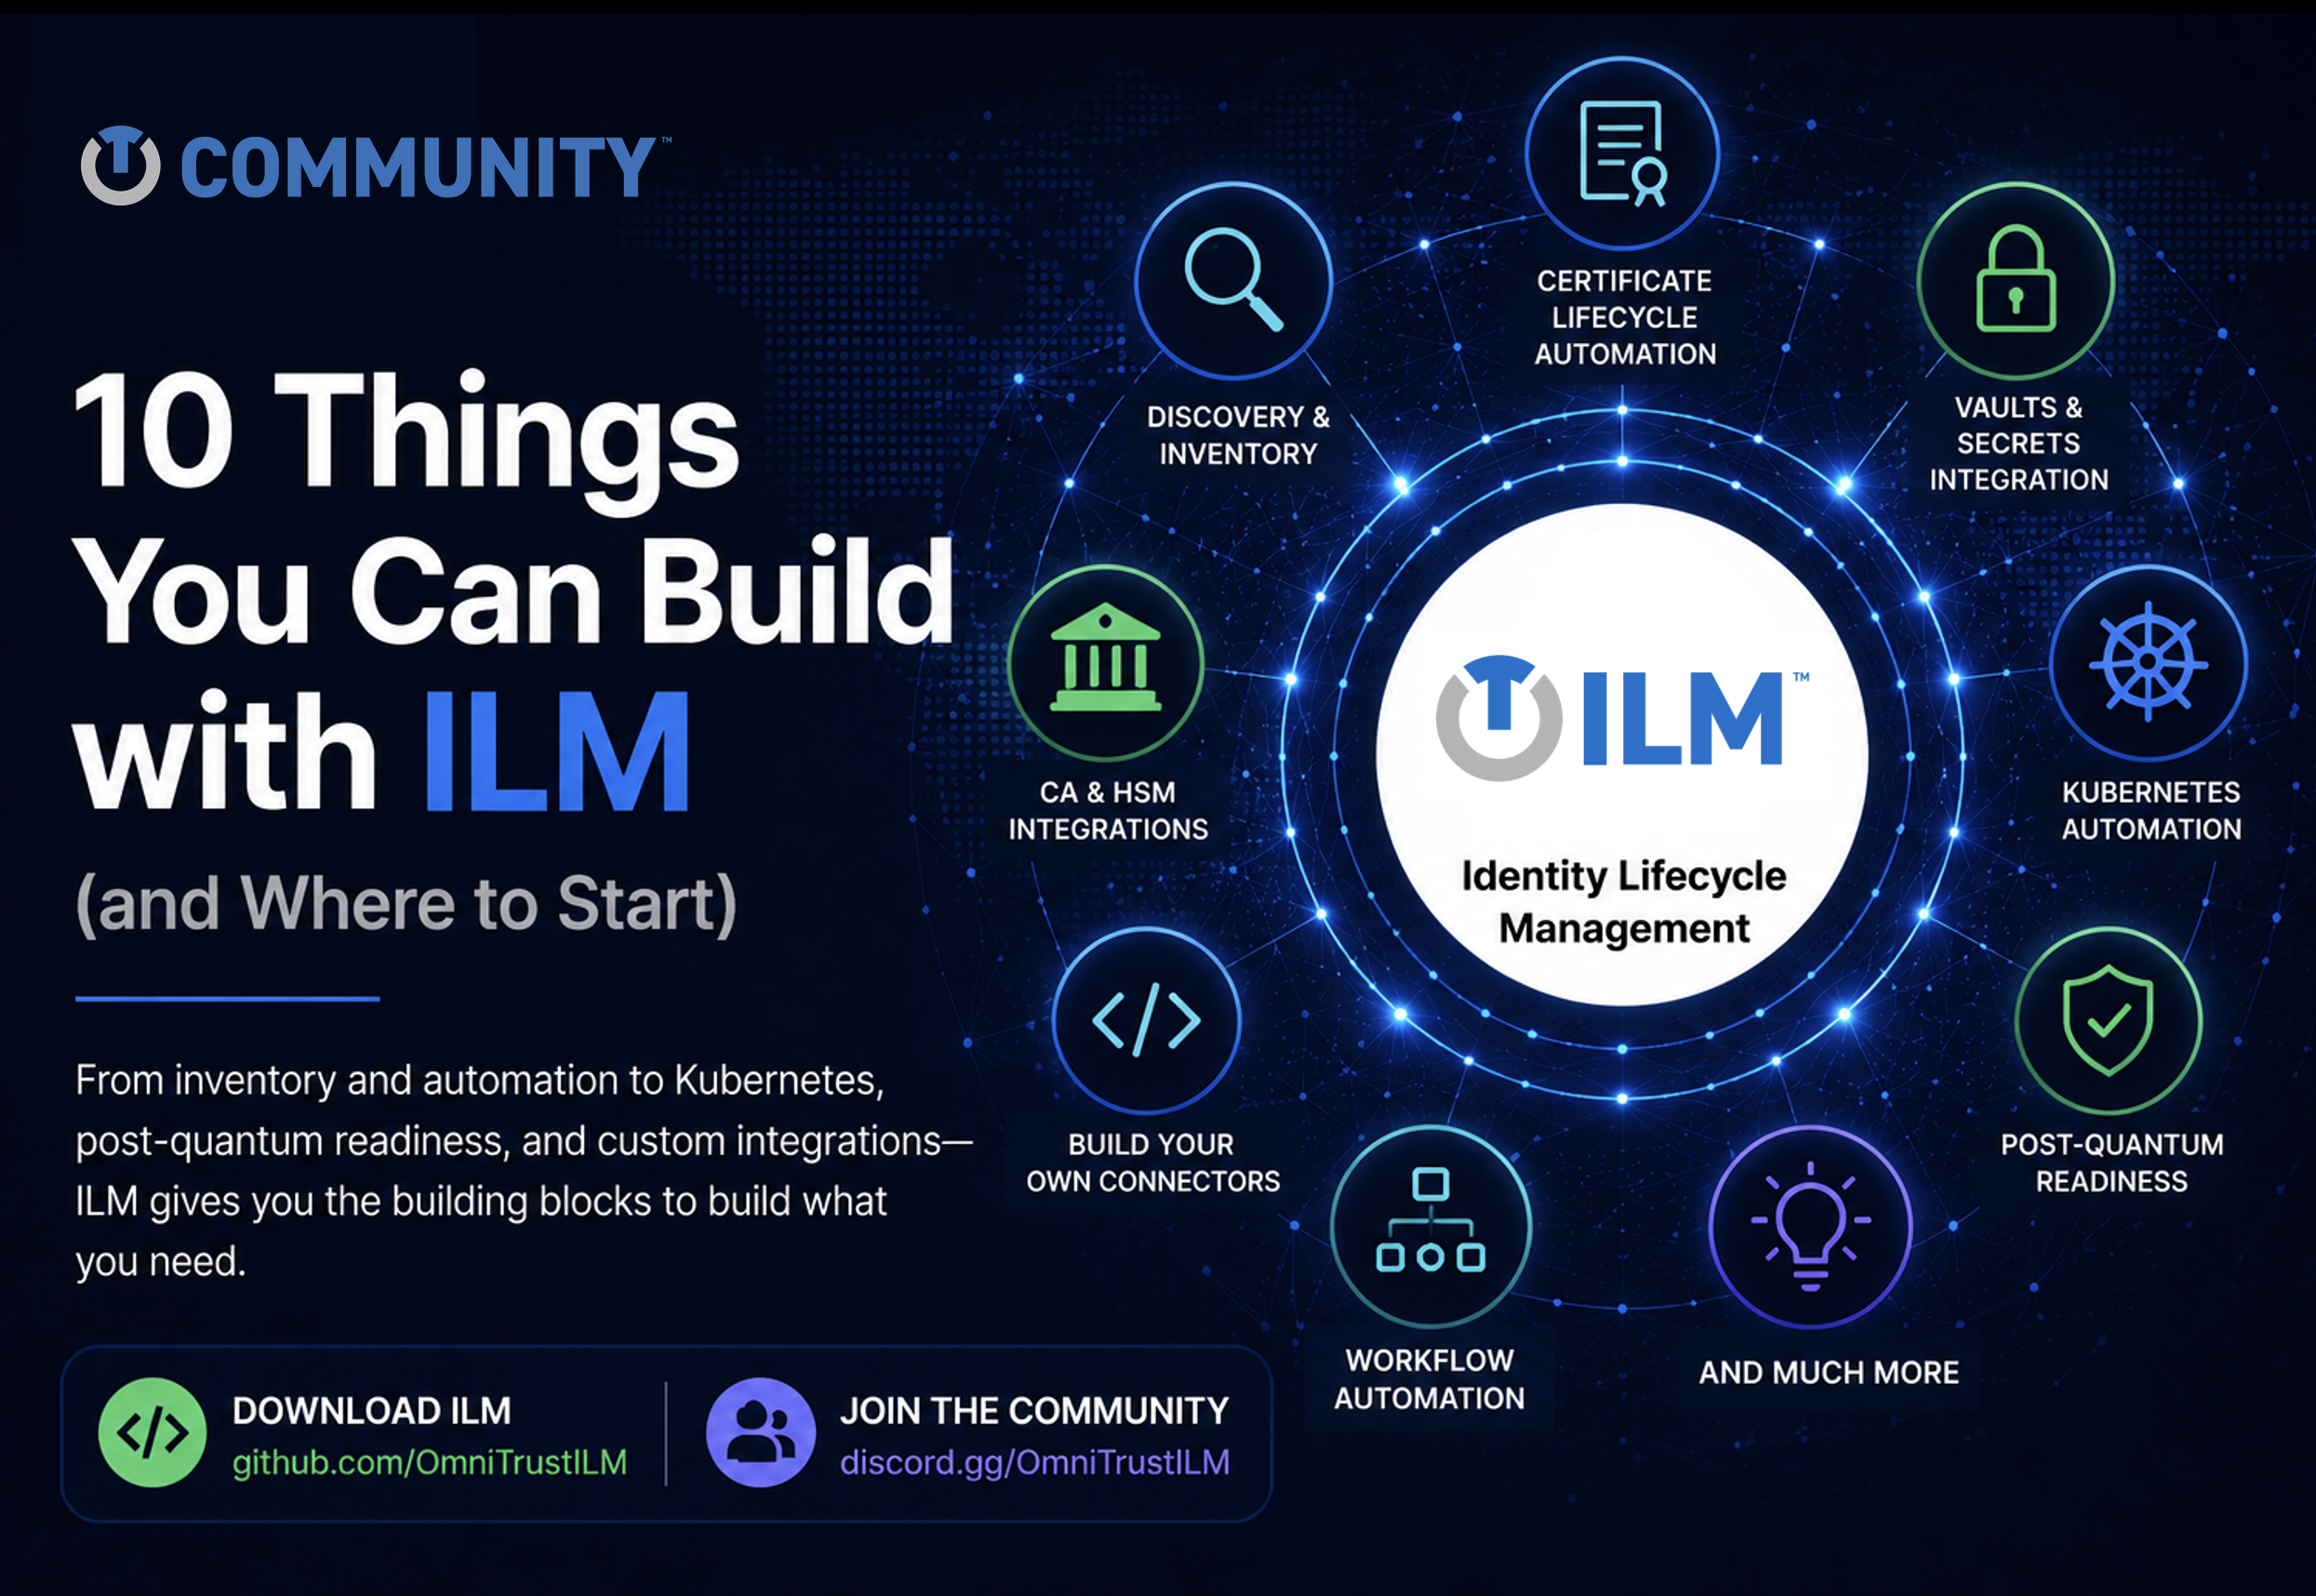
10 Things You Can Build with ILM (Where to Start)
Certificate Lifecycle & Automation
,
PKI & Cryptographic Governance
,
Post-Quantum & Crypto Agility
Jakub Moravek
July 14, 2026
EU CRA Tales From The Trenches #3 – Why Security Maturity is Not Enough for CRA Readiness
Executive Viewpoints
,
Industry Insights
,
Lifecycle Lessons
,
Trust Lifecycle Management
NP
Nick Parnaby
July 9, 2026
Why We Open-Sourced ILM
PKI & Cryptographic Governance
,
Post-Quantum & Crypto Agility
,
Trust Lifecycle Management
Roman Cinkais
July 6, 2026
Contact Us
Home
Platform
Resources
Our Industries
Our Solutions
Company
Trust Lifecycle Management
AI Lifecycle Management (ALM)
Identity Lifecycle Management (ILM)
Device Lifecycle Management (DLM)
Certify
Trust Lifecycle Management
AI Lifecycle Management (ALM)
Identity Lifecycle Management (ILM)
Device Lifecycle Management (DLM)
Certify
Case Studies
OmniTrust Blog
Resource Library
Case Studies
OmniTrust Blog
Resource Library
Aerospace & Defense
Automotive & Transportation
Energy, Oil & Gas
Financial Services
Healthcare & MedTech
Industrial, Manufacturing & OT
Power & Utilities
Semiconductors & Hi-Tech
Telecom, Cloud & AI
Aerospace & Defense
Automotive & Transportation
Energy, Oil & Gas
Financial Services
Healthcare & MedTech
Industrial, Manufacturing & OT
Power & Utilities
Semiconductors & Hi-Tech
Telecom, Cloud & AI
Connected Cities Trust Infrastructure
Enable Zero-Trust Operations Across Domains
Enterprise AI Discovery & Shadow AI Control
Enterprise Cryptographic Discovery & CBOM
Lifecycle Compliance & Regulatory Assurance
Orchestrate Secrets, Keys & Cryptographic Trust at Scale
Post-Quantum & Crypto Agility Readiness
Secure Software & Firmware Signing
Secure Supply Chain & Manufacturing Trust
TrafficAuth – Trusted Mobility Infrastructure
Zero-Trust Identity & Credential Management
Connected Cities Trust Infrastructure
Enable Zero-Trust Operations Across Domains
Enterprise AI Discovery & Shadow AI Control
Enterprise Cryptographic Discovery & CBOM
Lifecycle Compliance & Regulatory Assurance
Orchestrate Secrets, Keys & Cryptographic Trust at Scale
Post-Quantum & Crypto Agility Readiness
Secure Software & Firmware Signing
Secure Supply Chain & Manufacturing Trust
TrafficAuth – Trusted Mobility Infrastructure
Zero-Trust Identity & Credential Management
About Us
Careers
Events
Media & Press
Meet Our Leaders
Partners
About Us
Careers
Events
Media & Press
Meet Our Leaders
Partners
Search