Resource Library
Explore OmniTrust insights designed to help leaders navigate the evolving trust and landscape. This library brings together our latest white papers, on-demand webinars, and event content, along with practical tools to support decision-making. Included is our PKI Maturity Model self-assessment, which allows customers and prospects to benchmark their current PKI posture against leading practices and understand what capabilities are needed to stay ahead as the attack surface continues to expand.
Shift-Left Trust: Embedded Security Validation
Move embedded trust validation earlier. Discover how OmniTrust, Synopsys and Infineon enable secure boot, root of trust, HSM/SHE services and provisioning to be tested in virtual development before physical hardware is available.
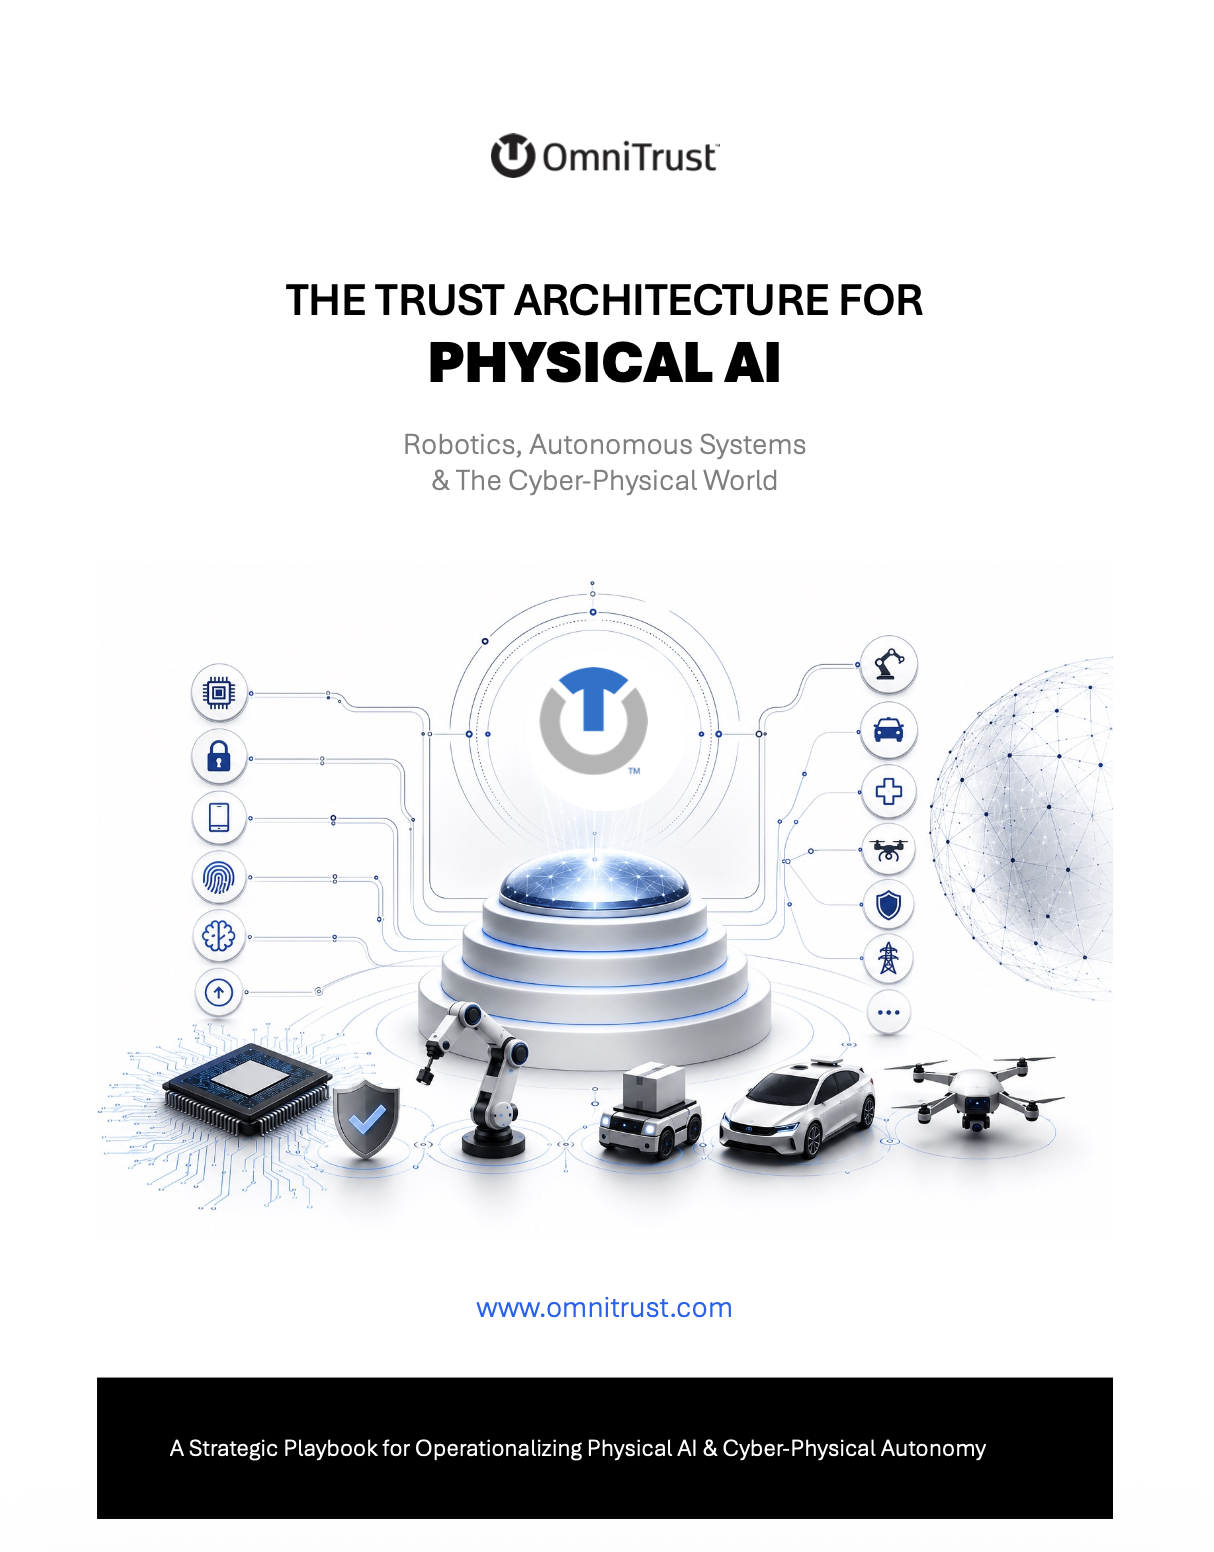
Building Trust for the Age of Physical AI
Physical AI is moving intelligence beyond software and into robots, vehicles, industrial systems and autonomous machines. This whitepaper introduces a Trust Infrastructure approach for securing these systems across hardware, identity, software, AI models, cryptography and physical execution — from silicon to autonomous operations.
The Switzerland Principle: Enterprise AI Control | OmniTrust
AI is evolving too quickly to lock your enterprise into one model, vendor, or infrastructure stack. The Switzerland Principle introduces a different approach: stay neutral enough to preserve choice, agile enough to adopt better technology as it emerges, and firmly in control of the data, identity, policy, economics, and operational advantage that should remain yours.
From Certificate Lifecycle Management to Cryptographic Governance
An executive guide to enterprise cryptographic governance — helping organizations inventory, govern, and future-proof cryptography in the era of post-quantum security.
50 min
The Future of Trust at the Physical Edge
Implementing zero trust principles in edge computing
45 min
Compliance Frameworks for Embedded Security
Navigating regulatory requirements across industries
60 min
The Future of Trust at the Physical Edge
Technical workshop on post-quantum cryptography transition
Self-Assessments
Quickly benchmark your PKI maturity and use the model as an ongoing reference to measure progress, align stakeholders, and prioritize future improvements.
Shift-Left Trust: Embedded Security Validation
Move embedded trust validation earlier. Discover how OmniTrust, Synopsys and Infineon enable secure boot, root of trust, HSM/SHE services and provisioning to be tested in virtual development before physical hardware is available.
Building Trust for the Age of Physical AI
Physical AI is moving intelligence beyond software and into robots, vehicles, industrial systems and autonomous machines. This whitepaper introduces a Trust Infrastructure approach for securing these systems across hardware, identity, software, AI models, cryptography and physical execution — from silicon to autonomous operations.
The Switzerland Principle: Enterprise AI Control | OmniTrust
AI is evolving too quickly to lock your enterprise into one model, vendor, or infrastructure stack. The Switzerland Principle introduces a different approach: stay neutral enough to preserve choice, agile enough to adopt better technology as it emerges, and firmly in control of the data, identity, policy, economics, and operational advantage that should remain yours.
From Certificate Lifecycle Management to Cryptographic Governance
An executive guide to enterprise cryptographic governance — helping organizations inventory, govern, and future-proof cryptography in the era of post-quantum security.
A global electric vehicle manufacturer needed to support ISO 15118-compliant Plug & Charge across its growing network of vehicles, charge points, and service providers. As EV adoption accelerated, the company required a unified trust infrastructure that could authenticate vehicles, chargers, and mobility service providers automatically — eliminating user friction while maintaining cryptographic control and compliance with international standards.
Smart infrastructure operators face escalating risks as PLCs, SCADA systems, elevators, building management systems (BMS), and connected city services converge on digital networks. These assets are long-lived, safetycritical, and regulated under IEC 62443, SIL 3/4, and NIST SP 800-82. Challenges include legacy assets with expired credentials, PLC-driven elevators integrated into fire and BMS systems, and emergency phone lines converted to IP/VoIP, creating new attack surfaces. SCADA/DCS controllers managing power, water, and city services are also exposed to cyber and compliance risks, compounded by fragmented visibility across suppliers and infrastructure. To meet safety and regulatory demands, operators require a resilient, audit-ready trust foundation ensuring compliance and uptime.
A leading U.S. power utility needed to secure and modernize its digital trust infrastructure across IT and OT networks. With thousands of certificates, keys, and secrets spread across enterprise applications, SCADA devices, and mobile endpoints, the risk of outage, cyberattack, and compliance gaps was rising sharply. At the same time, the organization faced increasing regulatory pressure and had committed to a full digital transformation by 2030, requiring a more resilient, unified trust foundation.
OmniTrust helped a Tier-1 auto supplier secure ECU credentialing worldwide with automated key management, real-time validation, and full compliance across the vehicle manufacturing lifecycle.
Quickly benchmark your PKI maturity and use the model as an ongoing reference to measure progress, align stakeholders, and prioritize future improvements.